Cloud Banking: The Future of Banking, or What the Banking Sector Will Look Like in 2030
What's new: Unverifiable 2021-era statistics replaced with current sources, new sections on DORA, concentration risk and AI rules, a step-by-step migration plan, common mistakes and an FAQ.
Summarize with AI
Read summarized version with AI
- Cloud banking means running banking systems, from channels and data to payments and the core ledger, on cloud infrastructure; workloads move in a sequence, and the core usually goes last.
- Core banking is now sold as a service, and full migrations take years: Capital One spent eight years leaving eight data centers for AWS.
- DORA has applied since 17 January 2025, and in November 2025 EU supervisors designated 19 critical ICT providers, including AWS, Google Cloud and Microsoft, for direct oversight.
- The October 2025 AWS us-east-1 outage showed that concentration risk is real: map hidden single-region dependencies and test your exit and recovery plans.
- Plan per workload: map critical functions, classify data, pick rehost, replatform, refactor or replace, design for failure, write the exit strategy and assign a cost owner.
When we first published this article in 2022, the open question was whether banks would really move to the cloud. In 2026 that question is settled. Large banks have closed data centers, core banking is sold as a service, and European supervisors now oversee the biggest cloud providers directly. The questions that matter now are different: which workloads should move, how a bank stays in control of a provider it cannot easily leave, and what the bank of 2030 will need from its technology.
This guide explains how cloud banking works, what changed in regulation and in the market since 2022, the real benefits and the real risks, and a step-by-step way to plan a move. It is written for CTOs, heads of engineering and founders at banks, lenders and fintechs.
What is cloud banking?
Cloud banking means running banking systems, from the core ledger and payments to customer channels, data platforms and back-office tools, on cloud infrastructure instead of only on servers the bank owns and operates. The bank rents computing power, storage and managed services, or complete applications, from a provider and pays for what it uses.
In practice nobody moves "the bank" in one go. Workloads move in a sequence, and the order matters more than the destination. Today these are the parts of a bank that most often run in the cloud:
- Digital channels: mobile and web banking, customer portals, notifications.
- Data and analytics: data platforms, regulatory reporting, fraud and risk models, AI.
- Payments and integration: event streaming, real-time transaction monitoring, API gateways for open banking.
- Onboarding and compliance: KYC and AML checks, case management, audit trails.
- Core banking: increasingly a cloud-native core bought as a service rather than the old core lifted onto rented servers.
Our view from 2022 still holds: the bank of 2030 will look very different from today's. Customers expect instant, always-on services, payments settle in seconds, and AI models need compute on demand. All of that assumes infrastructure that scales when needed and changes every week, not once a year.
How cloud banking works: service and deployment models
Providers such as Amazon Web Services, Microsoft Azure and Google Cloud run the physical infrastructure and rent it out. Banks consume it in three service models. Each model moves a different share of the work, and of the risk, to the provider.
| Model | What the provider runs | What the bank still owns | Typical banking use |
|---|---|---|---|
| IaaS (Infrastructure as a Service) | Data centers, hardware, networking, virtualization | Operating systems, middleware, applications, data, security configuration | Rehosting existing servers, disaster recovery sites, burst capacity |
| PaaS (Platform as a Service) | All of the above plus runtimes, managed databases, message queues, container platforms | Application code, data, identities and access rules | New digital channels, event streaming for payments, data platforms |
| SaaS (Software as a Service) | The complete application | Configuration, data, user access, integrations | CRM, HR, KYC screening, and increasingly the core banking system |
The biggest change since 2022 sits in the last row. Core banking is now sold as a service. Thought Machine positions its Vault Core as a cloud-native core with deployment flexibility across multi-cloud environments, and Mambu says its platform is used by financial institutions in more than 65 countries. For a new bank or a lender, buying a cloud core is now a realistic first option, not an experiment.
The way the infrastructure is shared is the second decision, usually called the deployment model.
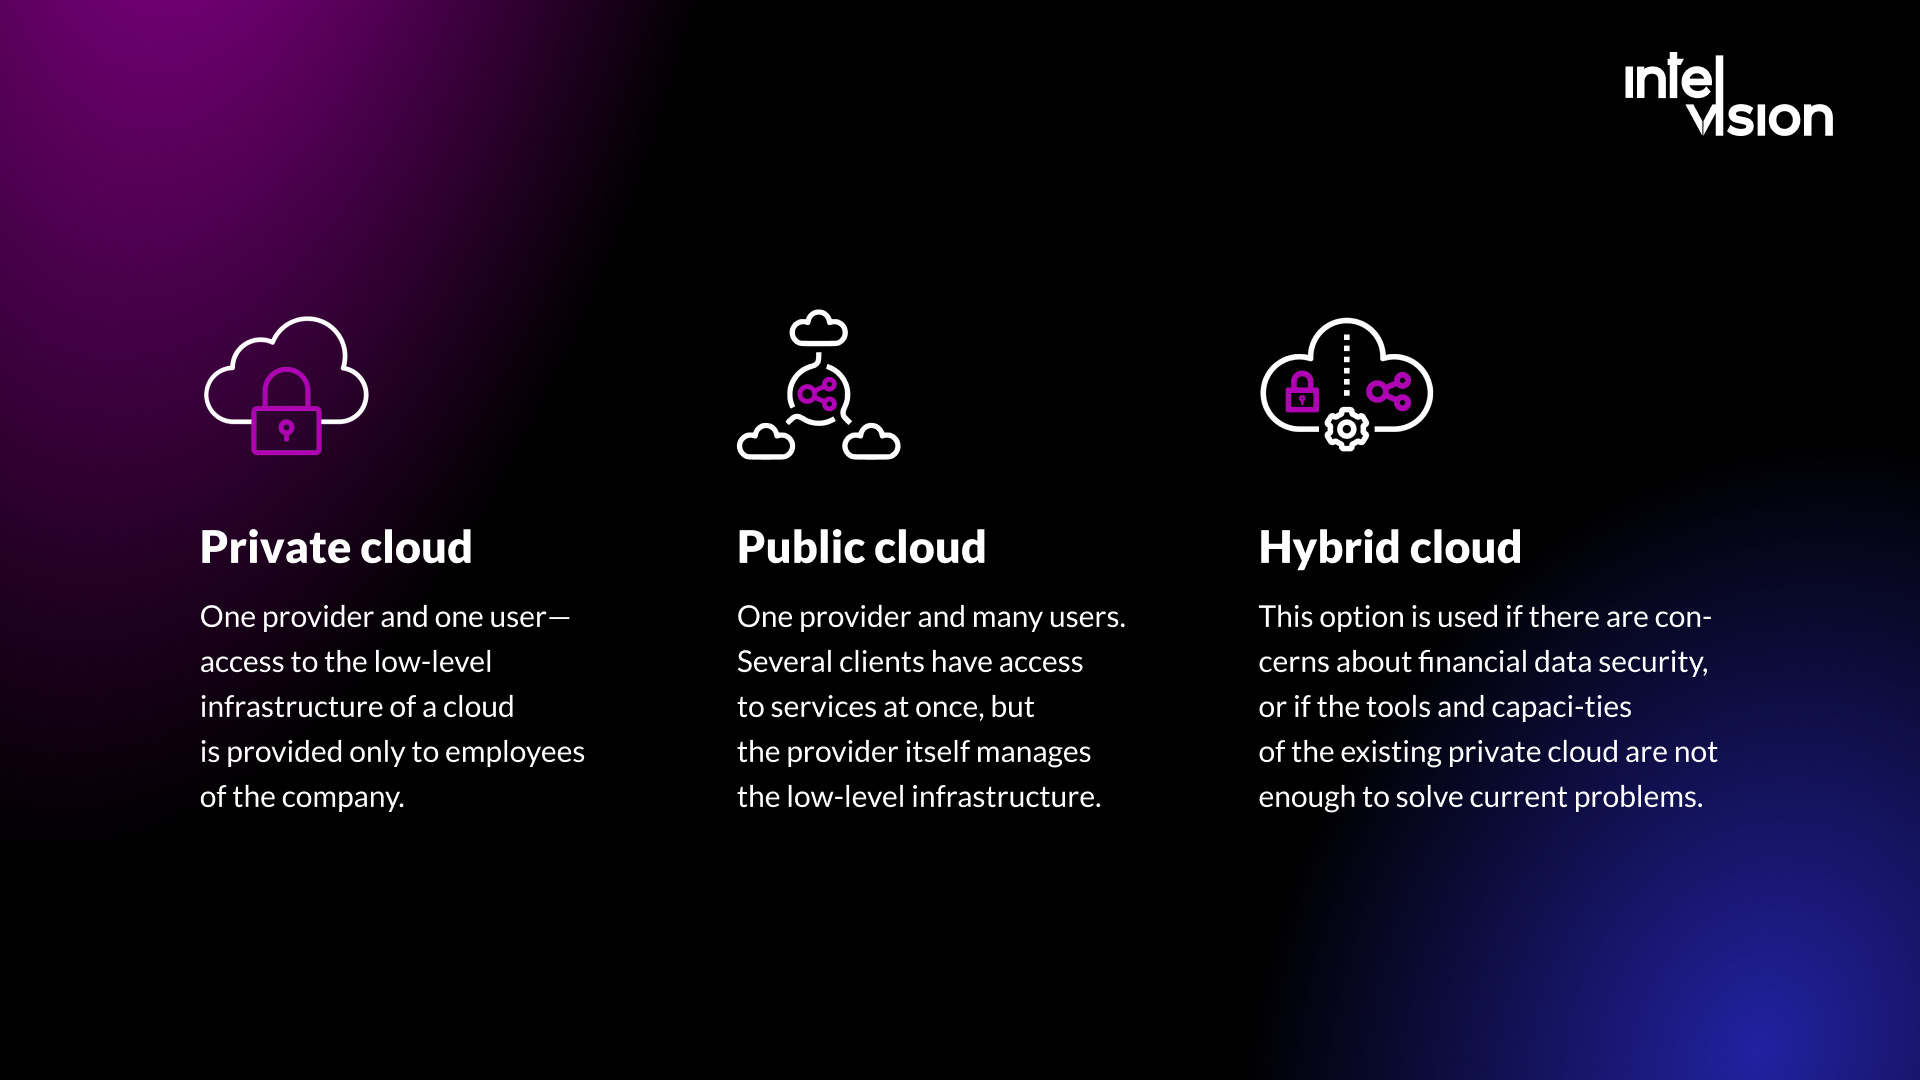
Private cloud
Infrastructure dedicated to one bank, in its own data center or hosted by a partner. The bank keeps the most control, and also carries the capacity planning and the cost of idle hardware.
Public cloud
One provider, many customers. The provider runs the shared infrastructure, and each customer is isolated logically. This is the fastest way to use managed services and scale on demand, and it is where concentration risk comes from.
Hybrid cloud
The most sensitive data and the legacy core stay in a private environment, while new channels, analytics and extra capacity run in the public cloud. For an incumbent bank this is often the practical starting point, because it lets the old and the new run side by side during a migration that takes years.
Multi-cloud and sovereign cloud
Multi-cloud means using more than one provider, either for resilience or to avoid depending on one vendor. Sovereign cloud offerings answer European concerns about data location and operational control. AWS, for example, now markets an independently operated European Sovereign Cloud. Sovereign options reduce some regulatory friction, but they do not remove the need for an exit plan.
Where banks stand in 2026
Full migrations have happened, and they took time. According to AWS's case study, Capital One began its technology transformation in 2012, spent eight years on the migration and exited eight on-premises data centers to run on AWS. That is the realistic scale for a large bank: close to a decade, not a single program.
The supplier market has grown with it. When the European Supervisory Authorities mapped the market in 2023, they found around 15,000 ICT third-party providers directly serving EU financial entities. In November 2025 they published the first list of critical ICT third-party providers under DORA: 19 companies, including Amazon Web Services, Google Cloud, Microsoft, Oracle, IBM, SAP, Equinix and Deutsche Telekom. Those providers are now overseen by EU supervisors directly, which tells you how central they have become to European finance.
Two forces keep pushing banks further:
- Real-time payments. Euro instant credit transfers make funds available to the payee within ten seconds, 24 hours a day, and the EU's Instant Payments Regulation of 13 March 2024 aims to make them standard. A ten-second, always-on payment rail does not fit systems built around nightly batches.
- AI. Fraud detection, credit decisioning support, document processing and internal copilots all need compute that scales up and down. The cost is now visible: the State of FinOps 2026 report, based on 1,192 respondents representing more than $83 billion of annual cloud spend, found that 98% of respondents now manage AI spend, up from 31% two years earlier.
Advantages of cloud-based banking
The benefits we listed in 2022 still hold. Four years of real migrations have sharpened them, and each comes with a condition.
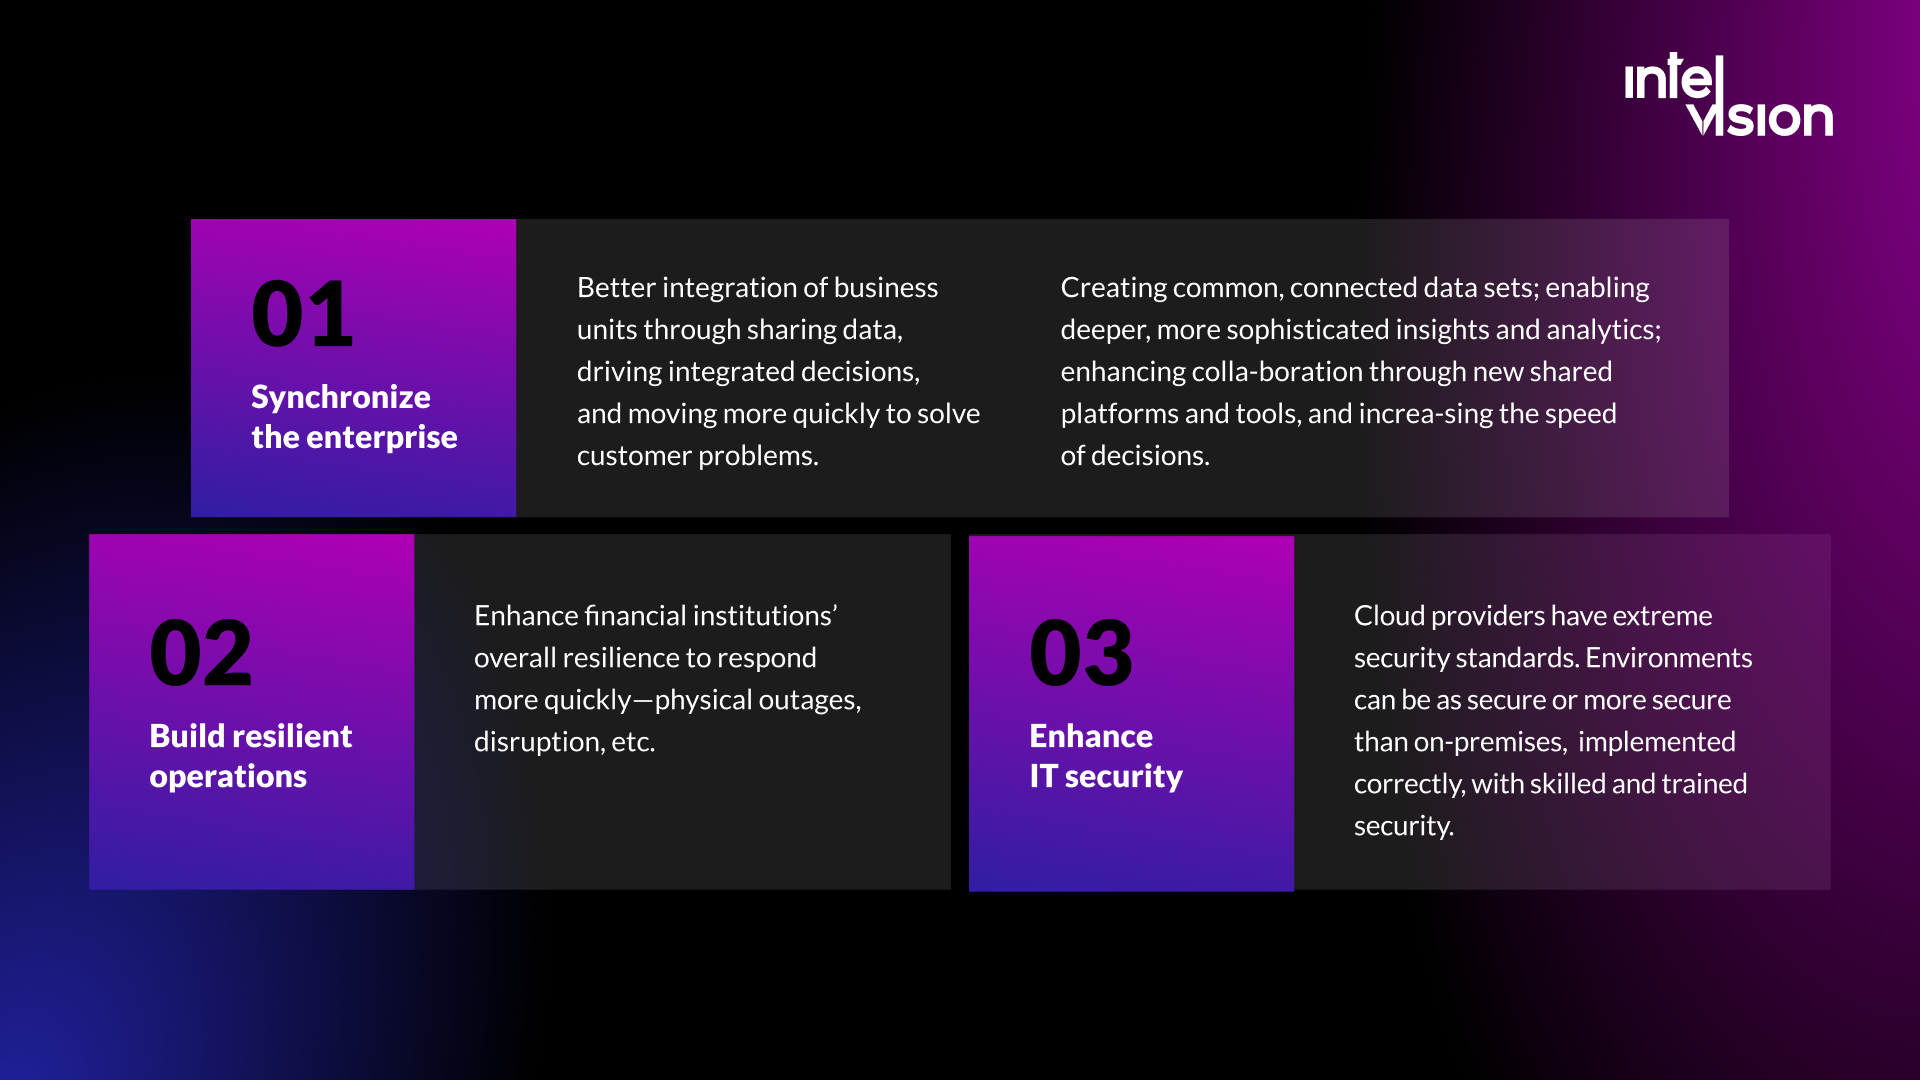
Synchronize the enterprise
- Business units share one data platform instead of copying data between systems, so product, risk, finance and customer service decide on the same numbers.
- Common, connected data sets make deeper analytics possible and shorten the path from a customer problem to a fix.
Condition: this only works if data ownership and access rules are designed first. Moving silos into the cloud gives you cloud silos.
Build resilient operations
- Applications can run across several availability zones or regions, with automated failover and backups that do not depend on one building.
- Recovery can be tested regularly, which is hard and expensive with physical standby sites.
Condition: the cloud does not make you resilient by default. Resilience has to be designed, paid for and tested, as the outages described below show.
Enhance IT security
- Cloud providers invest in physical security, patching and threat detection at a scale few banks can match. Implemented correctly, with skilled people, cloud environments can be as secure as on-premises ones or more so.
- Security is shared. The provider secures the infrastructure; the bank secures its configuration, identities, keys and data. Much of the day-to-day work sits on the bank's side.
Ship products faster
- Teams create environments in minutes and release more often, which shortens time to market for new accounts, cards and payment features.
- Payments, KYC and core functions can be bought as services and combined, so a new product does not start from the infrastructure.
Use data and AI
- Managed machine learning services and on-demand GPUs make fraud models, document processing and customer service automation practical without buying hardware for peak load.
Pay for what you use, if you manage it
- Maintaining your own hardware, software, staff and troubleshooting generates fixed costs. The cloud turns much of that into variable cost.
- Variable cost can also grow quietly. Without someone who owns cloud cost (FinOps), savings on hardware disappear into idle resources and oversized databases.
Risks and regulation: what changed since 2022
The biggest difference between 2022 and 2026 is regulation. Cloud is no longer a technical choice that compliance reviews at the end. It is a regulated dependency.
DORA in the EU
The Digital Operational Resilience Act has applied since 17 January 2025. It covers ICT risk management, ICT third-party risk, resilience testing, the reporting of major ICT incidents and the sharing of threat information, and it sets up the oversight framework for critical providers. For a bank or a regulated fintech this means, in practice:
- A register of information that lists every ICT contract and which functions depend on it.
- Contracts with the clauses DORA expects, including audit and access rights and exit terms.
- A tested exit strategy for providers that support critical or important functions.
- Incident classification and reporting that works across your own systems and your providers'.
The UK critical third parties regime
In the UK, the Bank of England, the PRA and the FCA published policy statement PS16/24 on 12 November 2024. The rules took effect on 1 January 2025, and the obligations apply to a provider once HM Treasury designates it as a critical third party. The regime adds oversight of providers; it does not remove a firm's own accountability for third-party risk.
Concentration risk is not theoretical
On 19 and 20 October 2025, AWS's N. Virginia region (us-east-1) had a major outage. AWS's post-event summary traces it to a latent race condition in the DNS management of DynamoDB that left a regional endpoint without IP addresses. The problem started at 11:48 PM PDT on 19 October and was fully resolved at 2:20 PM PDT on 20 October, after knock-on failures in EC2 instance launches, Network Load Balancer and Lambda. The lesson for banks is not "avoid the cloud". It is to know which of your services quietly depend on one region or one managed service, and to design and test for that failure.
AI rules for credit and risk
The EU AI Act lists AI systems used for credit scoring among high-risk use cases. Obligations for general-purpose AI models have applied since 2 August 2025. After the AI Omnibus entered into force on 27 July 2026, the high-risk obligations for Annex III use cases such as credit scoring apply from 2 December 2027. Banks building AI on cloud platforms now should design logging, data governance and human oversight into the architecture rather than retrofit them.
Key trends shaping banking toward 2030
- Hybrid and multi-cloud by design. In 2022 we noted that large banks were keeping their most sensitive data and critical infrastructure in a private cloud and connecting other services through the public cloud. That pattern has become the default for regulated workloads, now with explicit exit plans and second providers for the most critical functions.
- APIs as the integration layer. The role of APIs keeps growing. Open banking, embedded finance and banking-as-a-service all assume well-documented, secured APIs between the bank and its partners.
- Cloud-native, composable cores. New banks start on SaaS cores; incumbents run old and new cores in parallel and move products one by one.
- Real-time everything. Instant payments push fraud checks, liquidity monitoring and reporting toward streaming architectures instead of overnight batches.
- AI with evidence. AI moves from pilots into fraud, operations and customer service, under AI Act obligations and with cost tracked per use case.
- Sovereignty and exit plans. Where data lives and who operates the infrastructure become board-level questions, answered with sovereign offerings, encryption with bank-held keys and tested exit strategies.
How to plan a cloud move: a step-by-step approach
Whether you run an incumbent bank or a fintech that has outgrown its first setup, the sequence below keeps risk and cost under control.
- Map critical or important functions. List the business functions whose disruption would hurt customers or the bank, and the systems and providers behind each one. This map drives both the architecture and your DORA register.
- Classify data. Decide which data may live where, under which encryption and key management, and which residency rules apply.
- Choose a pattern per workload, not for the whole bank. Use the table below.
- Design for failure. Decide recovery time and recovery point objectives per function, then design zones, regions and, where needed, a second provider to meet them.
- Write the exit strategy before you sign. Data export formats, contract terms, the effort to move, and who would do it.
- Build the cost model. Include run costs, data transfer, licences, people and the period of running old and new systems in parallel. Assign a FinOps owner.
- Migrate in slices. Move one product or channel at a time behind stable APIs, and retire the old path only when the new one has run in production.
- Operate with evidence. Incident reporting, resilience tests and access reviews should produce the records supervisors ask for, as a by-product of daily work.
| Pattern | What it means | When it fits | Main risk |
|---|---|---|---|
| Rehost | Move servers as they are | Exiting a data center on a deadline; disaster recovery | Same architecture, often higher cost |
| Replatform | Move to managed databases, containers and queues with small code changes | Stable applications that need better operations | Hidden dependencies on old infrastructure |
| Refactor | Redesign into services and event streams | Payments, fraud and channels that must scale and change often | Time, and the skills to run distributed systems |
| Replace | Buy a SaaS product, including a SaaS core | Commodity functions and new products | Vendor lock-in and data portability |
Common mistakes to avoid
- Treating the cloud as a data center somewhere else. Rehosting everything moves the old architecture and its problems, and the bill often goes up.
- Starting with the core. The core is the hardest and riskiest system to move. Channels, data and payments usually deliver value sooner and teach the team how to run in the cloud.
- Contracting before mapping. Signing with a provider before you know which critical functions depend on it makes DORA compliance a retrofit.
- Hidden single-region dependencies. A managed service, an identity provider or a DNS setup can tie a "multi-region" system to one region.
- Underestimating the shared responsibility model. Misconfigured access, unmanaged keys and over-privileged accounts are the bank's problem, not the provider's.
- Nobody owns cost. Without FinOps, idle environments and oversized resources erase the savings.
- Leaving compliance to the end. Logging, audit trails and access reviews are far cheaper to design in than to add later.
What we have built for fintech teams
At Intelvision we work with banks, lenders and payment companies on the parts of this journey where engineering decides the outcome. Two published examples from our fintech work:
- Real-time payment monitoring. For a licensed digital payments company in the DACH region, a six-person team built a stream-based payments dashboard with Node.js, React, Kafka, Redis and TimescaleDB on Azure. Report generation went from 2 days to minutes, anomaly response became 4x faster, and the platform covers 100% of live transaction flows.
- Compliance automation in onboarding. For a digital lender in the EU, a team assembled in two weeks automated KYC and AML checks on a Python, React, Kafka and AWS stack with the ComplyAdvantage API. Onboarding time fell from 48 hours to 2 hours, and compliance staffing needs dropped by 40%.
If you are planning a migration, our migration and modernization teams and cloud engineers can do the work inside your process. If the architecture itself is in question, a software architecture review gives you a ranked, costed path before you commit. For the compliance side, see our guide to RegTech in banking.
What the bank of 2030 will look like
The benefits of banking on the cloud are now well established: faster product development, systems that scale with demand, better use of data and less hardware to own and maintain. So are the limits: concentration risk, regulation that follows the data, and costs that need an owner.
The bank of 2030 will most likely run on several providers and a mix of models, with a cloud-native core or a clear path to one, real-time payments and fraud checks, AI in daily operations under clear rules, and an exit plan for every critical dependency. The banks and fintechs that get there first will be the ones that treat the cloud as an operating model, not a hosting decision.
If you need help building or modernizing a cloud banking product, tell us about it. You get a direct answer on whether we can help and what should happen first.
Sources
- AWS: Capital One case study
- ESAs: Report on the landscape of ICT third-party providers in the EU (2023)
- EBA: DORA oversight of critical ICT third-party providers
- ESAs: List of designated critical ICT third-party providers
- EIOPA: Digital Operational Resilience Act (DORA)
- Bank of England: PS16/24 Critical third parties to the UK financial sector
- AWS: Summary of the Amazon DynamoDB service disruption in the N. Virginia region
- European Commission: AI Act regulatory framework
- FinOps Foundation: State of FinOps 2026
- ECB: Instant payments
- Thought Machine: Vault Core
- Mambu
- AWS: European digital sovereignty
Read Intelvision often? Add us as a preferred source in Google Search.
Add to preferred sources